Siber Güvenlik Haberleri

Güvenilir yayınlardan canlı haberler, DayBreach CVE verileriyle eşleştirilmiş olarak.

Rapid728 gün önce

CVE-2026-94127: Critical Unauthenticated RCE in F5 BIG-IP APM

OverviewOn September 22, 2026, F5 published a security advisory for CVE-2026-94127, a critical heap-based buffer overflow vulnerability affecting F5 BIG-IP Access Policy Manager (APM). The vulnerability has a CVSS v3.1 score of 9.8. An unauthenticated attacker with network access to an affected virtual server may be able to achieve remote code execution (RCE) by sending specifically crafted traffic.BIG-IP APM provides identity-aware access control for applications and other corporate resources and can integrate with authentication technologies including OAuth, OpenID Connect, and SAML. CVE-202

İlişkili Şirketler
İlgili CVE'ler
Kaynakta oku
CERT Polska29 gün önce

MikroTrick: analiza techniczna, proces ujawnienia i zastosowanie agentów LLM

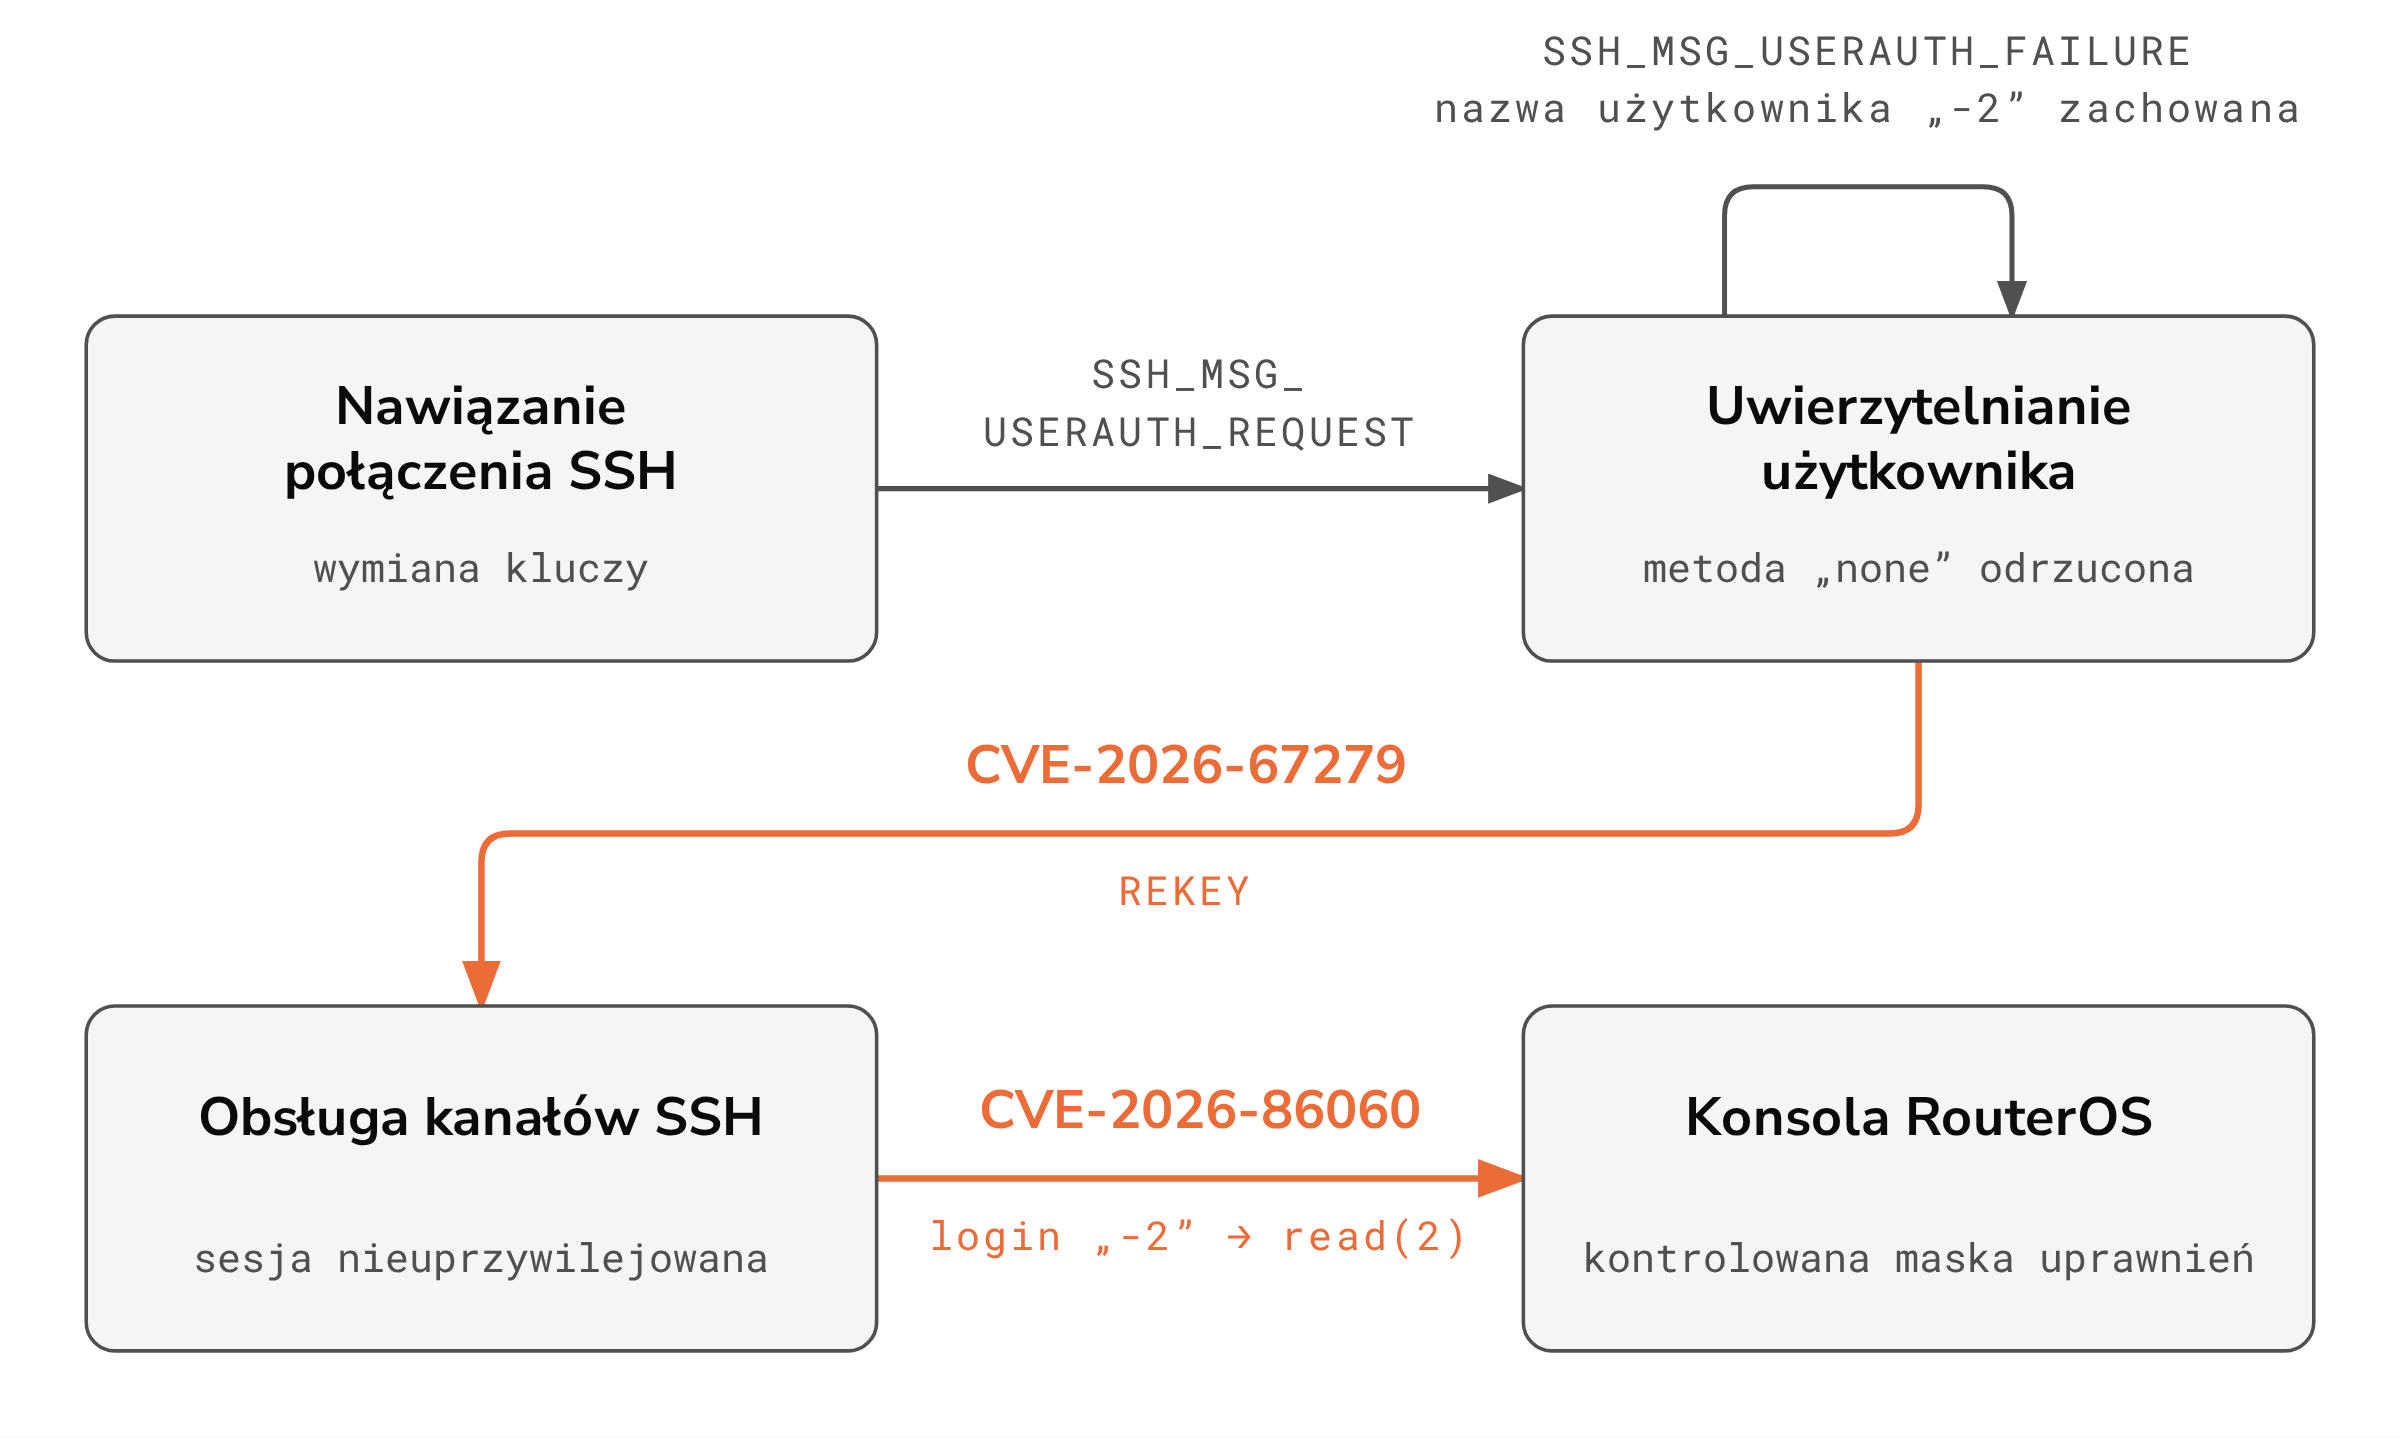
Opisujemy techniczne szczegóły łańcucha MikroTrick, złożonego z podatności CVE-2026-67279 i CVE-2026-86060, które w połączeniu pozwalały przejąć pełną kontrolę nad urządzeniem bez uwierzytelnienia. Wyjaśniamy mechanizm obserwowanych w internecie ataków, przebieg skoordynowanego ujawnienia obu podatności oraz praktyczną rolę agentów LLM w badaniach RouterOS.

İlişkili Şirketler
Kaynakta oku
Cisco Talos29 gün önce

The Closed Quorum: Inside the first reported autonomous AI C2 implant

CLOSEDQUORUM, a malware binary discovered through Cisco Talos’ CAIRN project, exhibits fully autonomous command and control (C2). It represents a shift in effort displacement for attackers, in which expanding portions of the attack chain can be executed without operator involvement.

İlişkili Şirketler
İlgili CVE'ler

Bu haber için doğrulanmış CVE bağlantısı bulunamadı.

Kaynakta oku

551-560 / 1404 haber gösteriliyor