

Siber Güvenlik Haberleri
Güvenilir yayınlardan canlı haberler, DayBreach CVE verileriyle eşleştirilmiş olarak.
Tüm kaynaklarArs Technica · 67BleepingComputer · 182CERT Polska · 78Cisco Talos · 49CrowdStrike · 35Dark Reading · 76DataBreaches.net · 35Krebs on Security · 14Microsoft Security Blog · 38Proofpoint · 37Rapid7 · 70SANS Internet Storm Center · 57Security.NL · 315SecurityWeek · 87SentinelOne · 33The Cyber Express · 70TheCyberThrone · 60The Hacker News · 314The Record · 48Unit 42 · 48






When Business Email Compromise Starts Rewriting Reality
Business Email Compromise (BEC) operates on a familiar playbook. Threat actors breach a mailbox, silently monitor operations, map approval chains, and ultimately exploit that access to divert funds or exfiltrate sensitive assets.This dynamic is central to our analysis as we kick off a series around Rapid7's collaborative research with Zimbra; upcoming installments will explore technical details and broader findings based within the Zimbra Collaboration Suite. Our investigation disrupted the traditional BEC model in unexpected ways. We uncovered over 50 vulnerabilities, and found that several a
Kaynakta oku


There's a new way to break RSA that's faster than anything we've seen before
Until now, cryptographers thought factoring was the only way to break RSA. Not anymore.
Kaynakta oku
FBI rushes to investigate if ShinyHunters hack of thousands of employees is real
It's unclear what will happen if FBI misses ShinyHunters' deadline.
Kaynakta oku
When Environment Variables Met Steganography: Inside a Reusable DCRat Delivery Chain
Learn how attackers combine environment variable staging and steganography in PNG files to deliver DCRat malware in memory.
Kaynakta oku
How dynamic application security testing validates risk at runtime
Security teams already have long queues of potential application vulnerabilities. The useful question is what happens next: can they see how a weakness behaves in a running application, reproduce the attack, and give developers enough evidence to fix it?Dynamic application security testing (DAST) helps answer those questions by testing applications as an attacker encounters them. The IDC MarketScape: Worldwide Dynamic Application Security Testing 2026 Vendor Assessment (Doc #US54119126, September 2026). The IDC MarketScape evaluated 16 vendors and named Rapid7 a Leader.We believe the result re


Kaynakta oku

Podatność w oprogramowaniu WEBCON BPS
W oprogramowaniu WEBCON BPS wykryto podatność błędnego uwierzytelniania (CVE-2026-92419).
Kaynakta oku
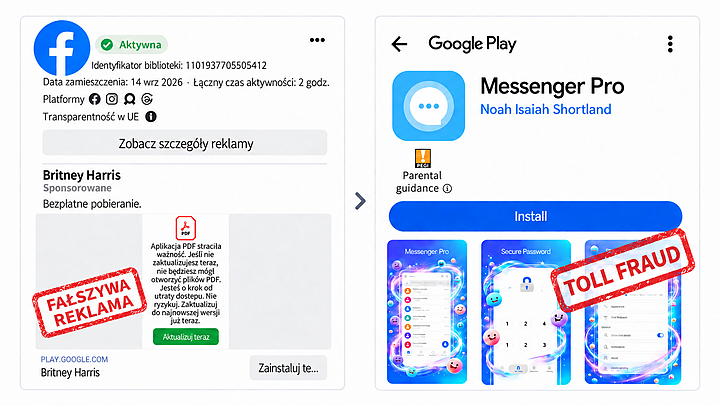
Fałszywe reklamy i złośliwe aplikacje - analiza operacji toll fraud
CERT Polska wykrył fałszywe reklamy na platformach Meta, które prowadziły do złośliwych aplikacji dostępnych w Google Play. Operacja toll fraud wymierzona była w polskich użytkowników Androida. Z 1235 zabezpieczonych reklam, 852 powiązaliśmy z 17 aplikacjami na podstawie wspólnego kodu lub infrastruktury. Odtworzyliśmy pełny łańcuch wykonania i zaobserwowaliśmy, jak aktywny serwer C2 przydzielał zadania związane z SMS Premium oraz płatnościami przez operatora.
Kaynakta oku
541-550 / 1404 haber gösteriliyor