
When Environment Variables Met Steganography: Inside a Reusable DCRat Delivery Chain
Learn how attackers combine environment variable staging and steganography in PNG files to deliver DCRat malware in memory.
Read at the source
Live news from trusted publications, matched against DayBreach CVE data.
Learn how attackers combine environment variable staging and steganography in PNG files to deliver DCRat malware in memory.
Security teams already have long queues of potential application vulnerabilities. The useful question is what happens next: can they see how a weakness behaves in a running application, reproduce the attack, and give developers enough evidence to fix it?Dynamic application security testing (DAST) helps answer those questions by testing applications as an attacker encounters them. The IDC MarketScape: Worldwide Dynamic Application Security Testing 2026 Vendor Assessment (Doc #US54119126, September 2026). The IDC MarketScape evaluated 16 vendors and named Rapid7 a Leader.We believe the result re

W oprogramowaniu WEBCON BPS wykryto podatność błędnego uwierzytelniania (CVE-2026-92419).
Read at the source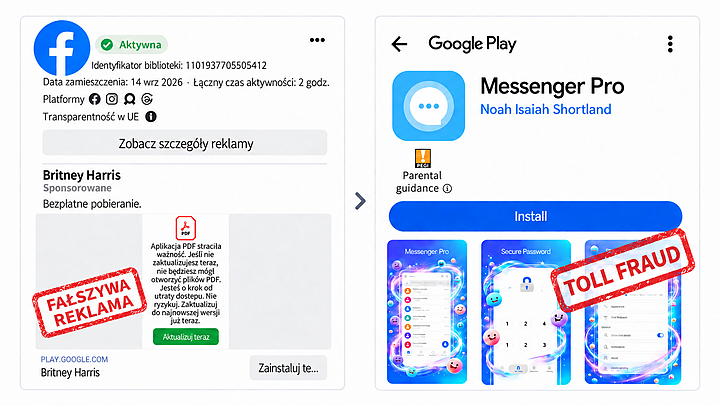
CERT Polska wykrył fałszywe reklamy na platformach Meta, które prowadziły do złośliwych aplikacji dostępnych w Google Play. Operacja toll fraud wymierzona była w polskich użytkowników Androida. Z 1235 zabezpieczonych reklam, 852 powiązaliśmy z 17 aplikacjami na podstawie wspólnego kodu lub infrastruktury. Odtworzyliśmy pełny łańcuch wykonania i zaobserwowaliśmy, jak aktywny serwer C2 przydzielał zadania związane z SMS Premium oraz płatnościami przez operatora.

OverviewOn September 22, 2026, F5 published a security advisory for CVE-2026-94127, a critical heap-based buffer overflow vulnerability affecting F5 BIG-IP Access Policy Manager (APM). The vulnerability has a CVSS v3.1 score of 9.8. An unauthenticated attacker with network access to an affected virtual server may be able to achieve remote code execution (RCE) by sending specifically crafted traffic.BIG-IP APM provides identity-aware access control for applications and other corporate resources and can integrate with authentication technologies including OAuth, OpenID Connect, and SAML. CVE-202
Read at the source
EvilTokens provided an end-to-end platform that makes mass compromises faster and easier.
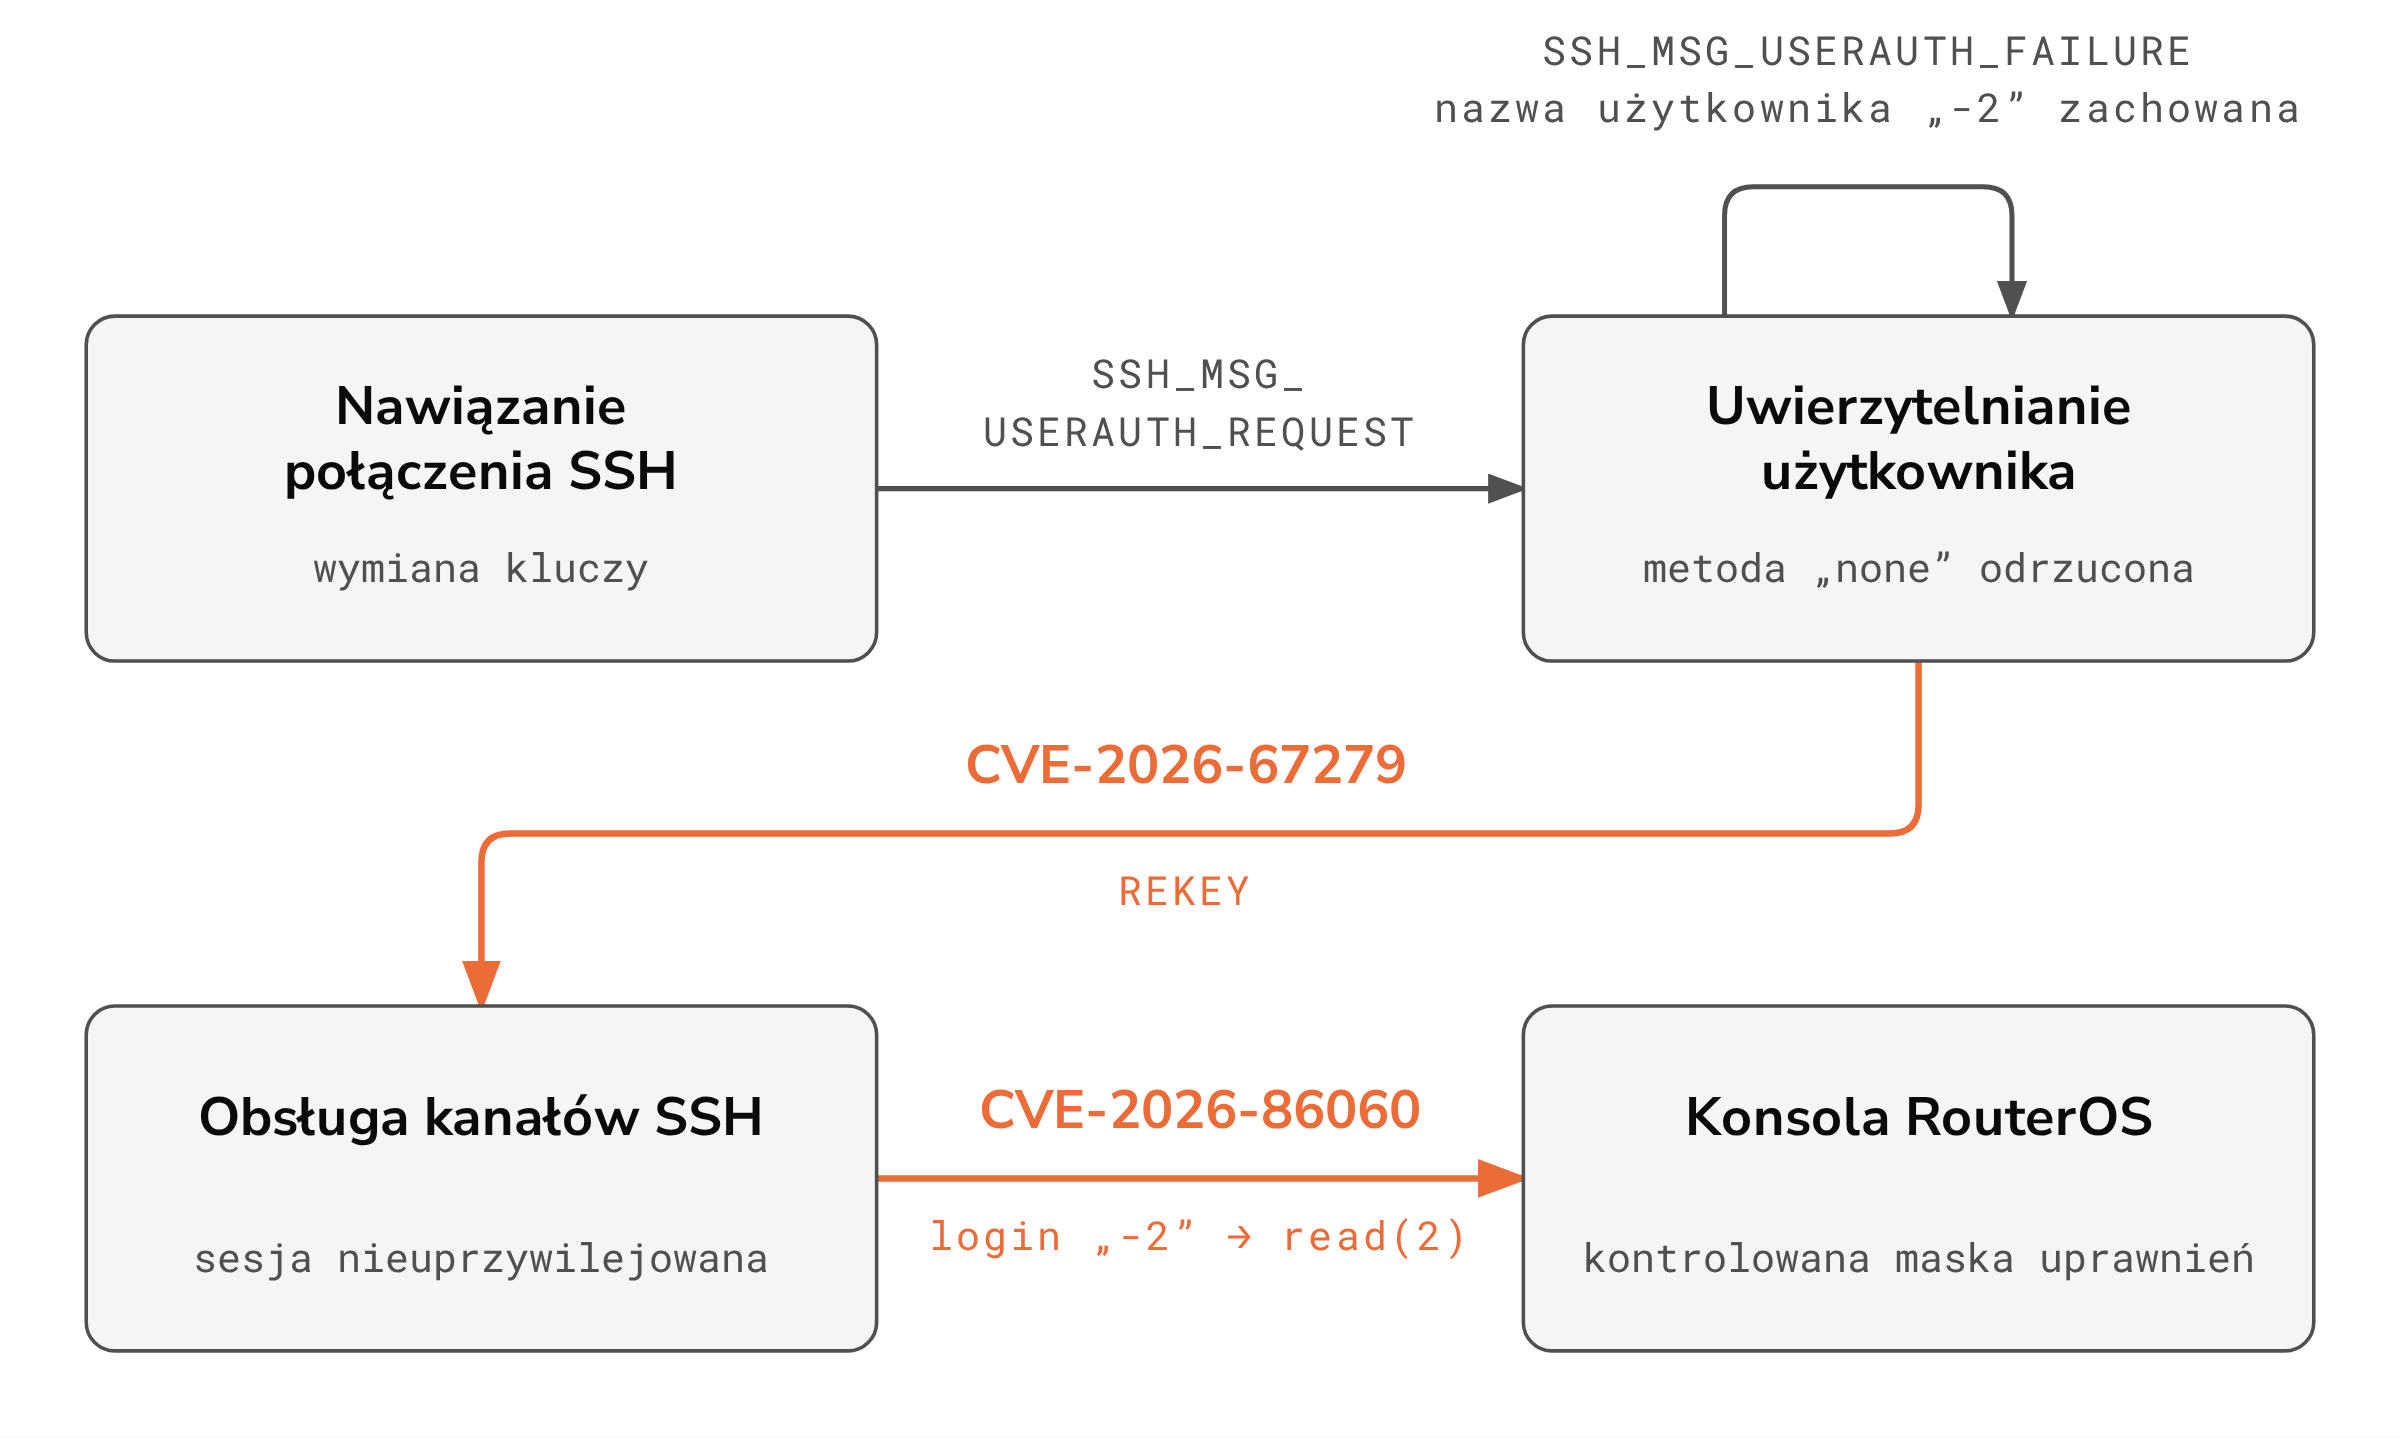
Opisujemy techniczne szczegóły łańcucha MikroTrick, złożonego z podatności CVE-2026-67279 i CVE-2026-86060, które w połączeniu pozwalały przejąć pełną kontrolę nad urządzeniem bez uwierzytelnienia. Wyjaśniamy mechanizm obserwowanych w internecie ataków, przebieg skoordynowanego ujawnienia obu podatności oraz praktyczną rolę agentów LLM w badaniach RouterOS.
Read at the source
811-820 / 1668 news items shown


