Security News

Live news from trusted publications, matched against DayBreach CVE data.

SecurityWeek13 d ago

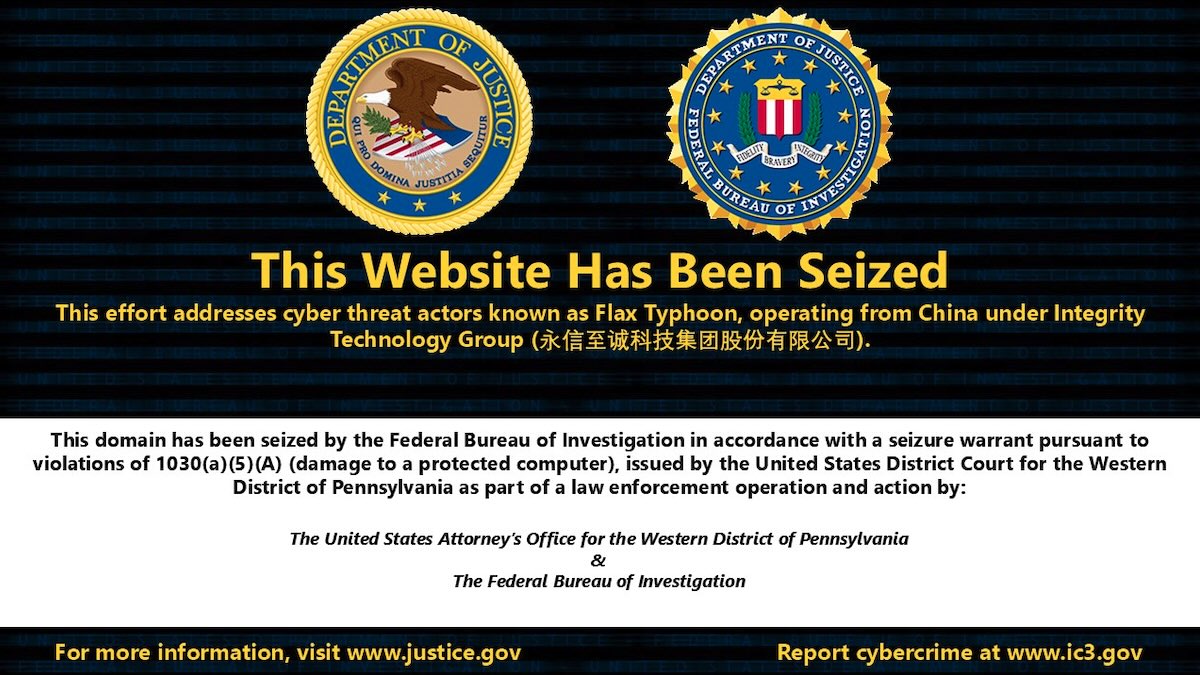
US Disrupts Chinese State-Sponsored Hacking Tools

Flax Typhoon and other APTs used MicroScan and FishHub to scan and hack US and foreign critical infrastructure. The post US Disrupts Chinese State-Sponsored Hacking Tools appeared first on SecurityWeek.

Related Companies
İlgili CVE'ler

No verified CVE link was found for this news item.

Read at the source
The Hacker News13 d ago

Three Teams Demonstrate Remote Hacks of Fully Patched Google Pixel 10 at Pwn2Own

Three research teams broke into Google's Pixel 10 on October 8 at Pwn2Own Ireland, a hacking contest in Cork whose rules require every target to be fully patched. The contest pays researchers to show working exploits and passes the flaws to the vendors. One of the three Pixel exploits earned Ikotas Labs $300,000, the contest's top prize, and made the team the overall winner. Trend Micro's Zero

Read at the source
The Hacker News13 d ago

Citrix Patches Critical NetScaler Flaw That Could Enable RCE in SAML Deployments

Citrix has released patches for yet another critical security flaw impacting NetScaler ADC and NetScaler Gateway that could result in remote code execution or denial-of-service (DoS) under certain conditions. "CVE-2026-107406 is a memory overflow vulnerability that may lead to remote code execution or denial-of-service under specific configuration conditions," Citrix said. The vulnerability

Read at the source
The Cyber Express13 d ago

Splunk Patches 22 Vulnerabilities, Including Critical Flaw With CVSS 9.8

Splunk has patched a large set of Splunk vulnerabilities in Splunk Enterprise, the most severe of which carries a CVSSv3.1 score of 9.8. The fixes are described in two advisories, SVD-2026-1001 and SVD-2026-1002, both published on October 7, 2026, and together they cover 22 CVE identifiers, CVE-2026-76264 through CVE-2026-76285. A security bulletin issued on October 9, 2026, rated the overall risk as medium and warned that a remote attacker could exploit some of the flaws to achieve remote code execution, denial of service, elevation of privilege, security restriction bypass, sensitive informa

Related Companies
Read at the source

661-670 / 1745 news items shown