

Kabinet wil inlichtingendiensten AIVD en MIVD meer bevoegdheden geven
Het kabinet wil inlichtingendiensten AIVD en MIVD meer bevoegdheden geven, zo blijkt uit een wetsvoorstel dat vandaag door de ...
Kaynakta oku
Güvenilir yayınlardan canlı haberler, DayBreach CVE verileriyle eşleştirilmiş olarak.
Het kabinet wil inlichtingendiensten AIVD en MIVD meer bevoegdheden geven, zo blijkt uit een wetsvoorstel dat vandaag door de ...

Security researcher Olivier Laflamme has disclosed two independent root remote code execution (RCE) chains affecting the Unitree G1 EDU, including a Bluetooth Low Energy (BLE) path that can reach root on the robot's Locomotion PC. The flaws are tracked as CVE-2026-76639 and CVE-2026-76640, with the first involving a network-adjacent path through chat_go and bashrunner and the
Kaynakta okuHet Nationaal Cyber Security Centrum (NCSC) waarschuwt organisaties dat er een grote kans is op misbruik van een kritieke ...
Kaynakta okuSoftwarebedrijf ServiceNow waarschuwt voor meerdere kritieke kwetsbaarheden in het eigen AI-platform waardoor ...
Kaynakta oku
An Identity Fabric knits fragmented identity systems into a coherent layer that observes how identities behave across applications, APIs, and infrastructure. As enterprise access spans more cloud services and automated workloads, identity security depends less on static configuration and more on runtime visibility. This article covers the architecture, the risks of unmanaged identities, and

ServiceNow has released patches for four security flaws impacting the ServiceNow AI Platform, three of them rated 10.0 on the CVSS scoring system and exploitable, in certain circumstances, by an unauthenticated attacker. The company said it deployed a security update to hosted instances and provided the update to its partners and self-hosted customers, which leaves organizations that run their
Kaynakta oku
This weekly roundup highlights a broad range of cybersecurity and technology developments affecting cloud identity infrastructure, social media platforms, businesses, digital assets, and international law enforcement. From a critical Microsoft Entra ID vulnerability exploited before remediation to a global crackdown on West African cybercrime networks, recent developments demonstrate how attackers continue to target both technical systems and human trust. The latest developments also show that cybersecurity risks are expanding alongside the rapid adoption of cloud services and artificial intel
Kaynakta oku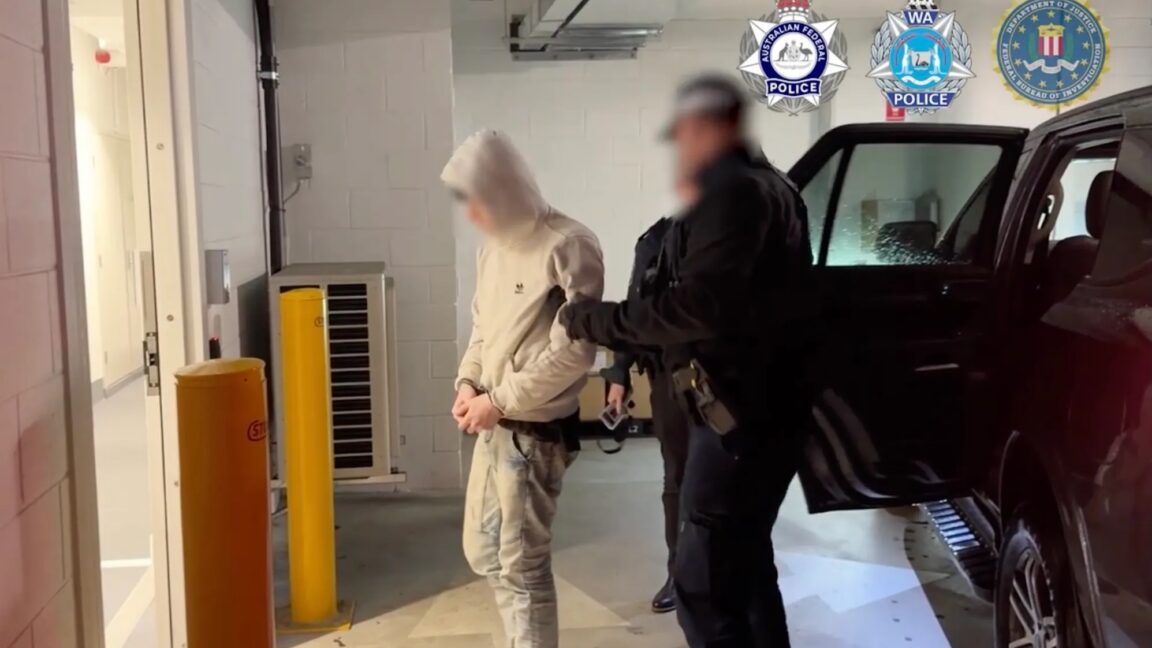
The group infected more than 1,000 organizations in a relentless supply-chain attack campaign.

VulnCheck has disclosed two previously undocumented factory implants in firmware for routers built by Shenzhen Zhibotong Electronics (ZBT), each of which gives an unauthenticated remote attacker the ability to run commands as root on affected devices. The implants, named SPEAKINGSTONE and DARKLANTERN by the company's zero-day research team, are tracked as CVE-2026-74232 and CVE-2026-74233.
Kaynakta oku
Overview On August 27, 2026, PaperCut Software published an urgent security advisory stating that it is investigating active exploitation of a vulnerability affecting PaperCut NG and PaperCut MF. PaperCut has confirmed customer incidents and is treating the issue as a security emergency. At the initial time of disclosure, the vulnerability had not been assigned a CVE identifier, and PaperCut had not publicly disclosed a CVSS score, vulnerability class, authentication requirements, or the technical details of the exploit path. However on August 28, the vendor assigned CVE-2026-81578 and CVE-202
Kaynakta oku711-720 / 1395 haber gösteriliyor


