Siber Güvenlik Haberleri

Güvenilir yayınlardan canlı haberler, DayBreach CVE verileriyle eşleştirilmiş olarak.

The Hacker News1 ay önce

Aurora Ransomware Operators Use Cursor AI in Attacks Against 10 Targets

Threat actors associated with Aurora (aka Aur0ra) ransomware have been observed using SpaceX's artificial intelligence (AI)-powered coding assistant Cursor to break into target networks, according to findings from CloudSEK and Gambit Security. The two independent analyses are based on exposed infrastructure associated with the Russian-speaking cybercrime group, leading to the discovery of its

İlişkili Şirketler
İlgili CVE'ler

Bu haber için doğrulanmış CVE bağlantısı bulunamadı.

Kaynakta oku
The Hacker News1 ay önce

Securing Claude Code: The New Compliance API, Local Visibility, and Identity Governance

Claude Code reads files, runs shell commands, invokes MCP tools, and acts through the credentials available on a developer’s machine. Anthropic’s new Compliance API endpoints give security teams their clearest view yet into that activity. They also expose a larger problem: activity logs alone cannot tell you whether an agent’s access is legitimate. AI has moved from the browser tab to the

İlişkili Şirketler
İlgili CVE'ler

Bu haber için doğrulanmış CVE bağlantısı bulunamadı.

Kaynakta oku
The Cyber Express1 ay önce

Boston Scientific Cyberattack Limited to Unauthorized Access on Certain On-Premises Systems

As per Boston Scientific’s Aug. 30 update, “the unauthorized activity is limited to certain on-premises systems,” providing the clearest indication yet of the scope of the cybersecurity incident that has disrupted the medical device maker’s global network and business operations. Boston Scientific said the investigation into the disruption remains ongoing, with third-party cybersecurity experts. Based on its investigation to date, the company said it has found no indication of unauthorized activity in its environment related to the incident since Aug. 25. The company also clarified that its cl

İlişkili Şirketler
İlgili CVE'ler

Bu haber için doğrulanmış CVE bağlantısı bulunamadı.

Kaynakta oku
The Cyber Express1 ay önce

PaperCut Issues Second Emergency Patch as Researchers Break Fix for Exploited Zero-Days

PaperCut released a second emergency patch last Friday, for two vulnerabilities in its NG and MF print management servers that attackers are already exploiting, after security researchers demonstrated that the vendor's first fix could be bypassed. The two flaws work as a chain. CVE-2026-81578, rated 8.8 on the CVSS scale, is an improper access control weakness in the PaperCut web management interface that lets unauthenticated remote requests reach administrative functions before the server finishes validating access. CVE-2026-82078, rated 9.4, is an unsafe dynamic class-loading flaw in the pro

İlişkili Şirketler
Kaynakta oku
The Cyber Express1 ay önce

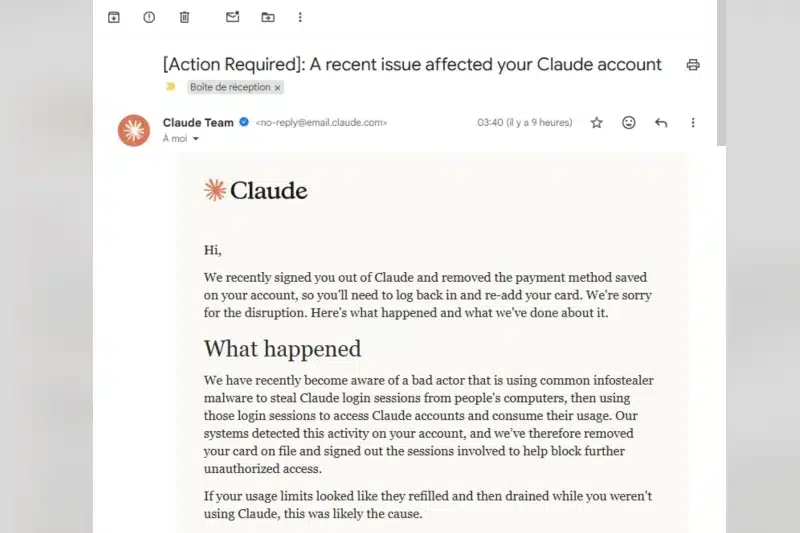
Anthropic Warns Commodity Infostealers Are Hijacking Claude Sessions to Drain Paid Usage

Anthropic warned users over the weekend that a threat actor is using widely available infostealer malware to hijack active Claude login sessions from infected computers, then using those sessions to run up victims' paid usage without ever needing a password or a two-factor code. The company said it identified six malware families in the campaign: Vidar, LummaC2, StealC, RedLine and Acreed on Windows, and Atomic Stealer, known as AMOS, on a smaller number of macOS machines. None are novel or bespoke. All are commodity stealers sold or rented on criminal dark web marketplaces, and all work the s

İlişkili Şirketler
İlgili CVE'ler

Bu haber için doğrulanmış CVE bağlantısı bulunamadı.

Kaynakta oku

671-680 / 1395 haber gösteriliyor