Siber Güvenlik Haberleri

Güvenilir yayınlardan canlı haberler, DayBreach CVE verileriyle eşleştirilmiş olarak.

The Hacker News2 ay önce

Anthropic Says Claude Mistook the Open Internet for a CTF and Breached Three Organizations

Anthropic on Thursday became the latest artificial intelligence (AI) company to reveal that three of its models, including Claude Opus 4.7, Mythos 5, and an unnamed research model, had breached three unnamed organizations during cybersecurity testing without its knowledge. The AI firm said the earliest incidents date back to April 2026, adding it made the discoveries after launching a "

İlişkili Şirketler
İlgili CVE'ler

Bu haber için doğrulanmış CVE bağlantısı bulunamadı.

Kaynakta oku
The Hacker News2 ay önce

DPRK-Linked macOS Malvertising Uses Fake Updates to Deliver Crypto-Stealing Malware

Threat actors with ties to North Korea have been attributed to a sophisticated macOS malvertising campaign that involves redirecting users to fake web pages displaying a full-screen non-existent update sequence to deliver malware as part of a new iteration of the long-running Contagious Interview campaign. The defining aspect of the attack is that bogus macOS software update screen stealthily

İlişkili Şirketler
İlgili CVE'ler

Bu haber için doğrulanmış CVE bağlantısı bulunamadı.

Kaynakta oku
Rapid72 ay önce

KindaRails2Shell: CVE-2026-66066, Critical Arbitrary File Read and Possible Remote Code Execution in Ruby on Rails

OverviewOn July 29, 2026, the Ruby on Rails project published a security advisory for CVE-2026-66066, a critical vulnerability affecting Active Storage image processing when used in conjunction with the libvips image processing library. The vulnerability has a CVSSv4 score of 9.5 and is classified as Initialization of a Resource with an Insecure Default (CWE-1188). An unauthenticated attacker may be able to leverage CVE-2026-66066 and read files accessible to the Rails application process, potentially exposing secrets that could enable remote code execution (RCE) or access to connected systems

İlgili CVE'ler
Kaynakta oku
Microsoft Security Blog2 ay önce

​​​​What’s new in Microsoft Security: July 2026

This month’s updates help security and IT teams secure their AI environments, use AI to defend, and strengthen the foundations that AI-powered operations depend on. The post ​​​​What’s new in Microsoft Security: July 2026 appeared first on Microsoft Security Blog.

İlişkili Şirketler
İlgili CVE'ler

Bu haber için doğrulanmış CVE bağlantısı bulunamadı.

Kaynakta oku
The Hacker News2 ay önce

ThreatsDay: AI-Powered Hacking, 370 Chrome Flaws, SonicWall Attacks, DNS Hijacking + 22 More Stories

A lot of security still comes down to trusting the wrong screen. This week, that screen might be a login page, an install guide, a recruiter call, or a familiar service behaving slightly wrong. Behind it: reused credentials, exposed systems, quiet loaders, abused trust, and exploit paths that should have been harder. Some defenses improved. The loose parts still got found first. Anyway,

Kaynakta oku
Rapid72 ay önce

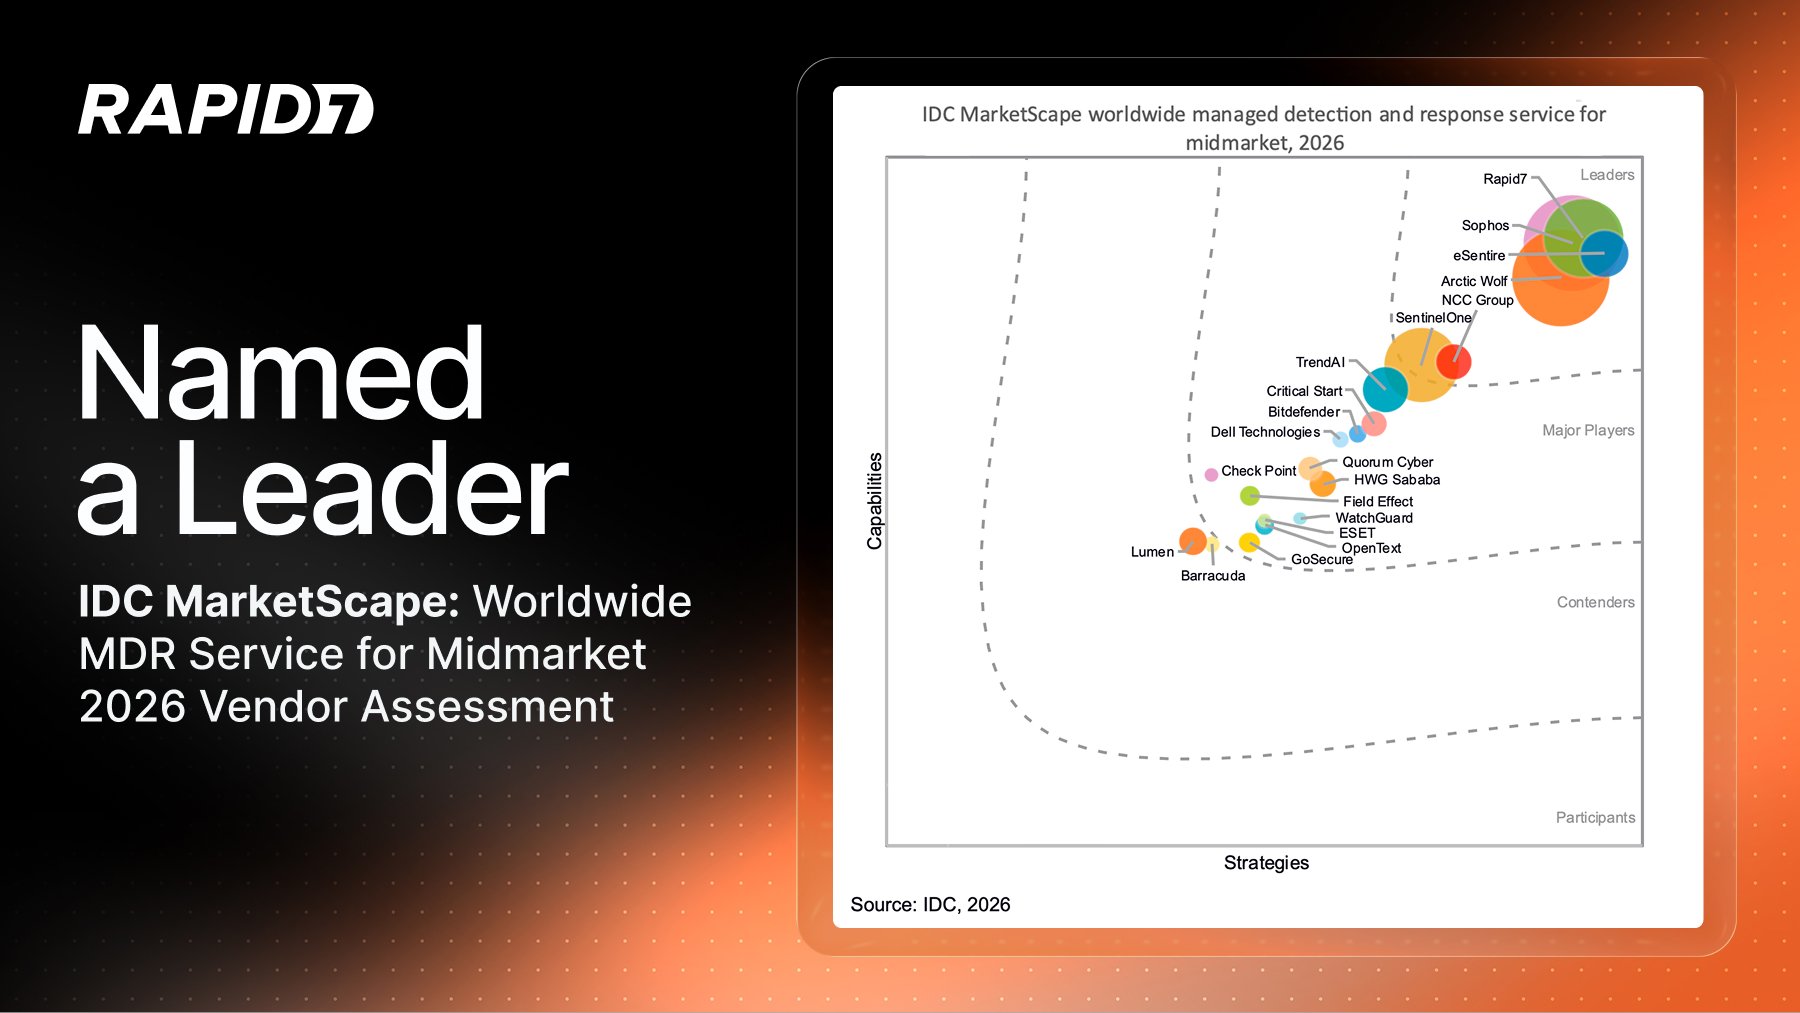
Rapid7 named a Leader in the IDC MarketScape: Worldwide MDR Service for Midmarket 2026 Vendor Assessment

IDC has named Rapid7 a Leader in the 2026 Worldwide Managed Detection and Response Service for Midmarket 2026 Vendor Assessment (Doc #US52992326, July 2026). We believe this recognition and research highlights where MDR is heading.Many security programs are still built around a reactive sequence of detect, triage, and respond, but the timelines surrounding modern attacks have changed too quickly for that model to hold up on its own. Time-to-exploit has dropped from two years to 22 hours, while eCrime breakout time now sits at 29 minutes. In an environment like that, a program moving at human s

İlişkili Şirketler
İlgili CVE'ler

Bu haber için doğrulanmış CVE bağlantısı bulunamadı.

Kaynakta oku

1161-1170 / 1370 haber gösteriliyor