Security News

Live news from trusted publications, matched against DayBreach CVE data.

The Cyber Express1 mo ago

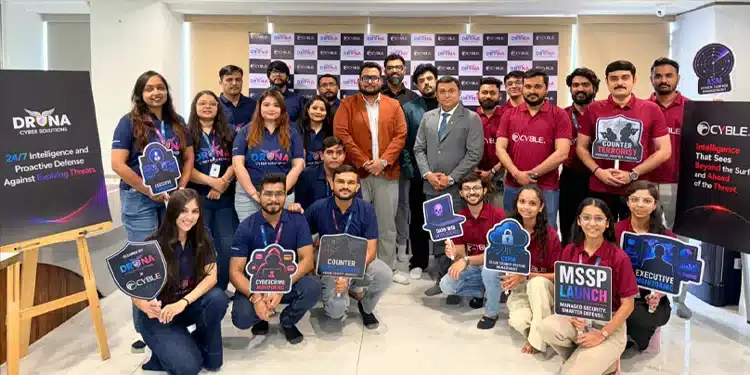
Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

AHMEDABAD (INDIA) — Cyble, the global AI-native cybersecurity company, and DRONA Cyber Solutions, the Ahmedabad-headquartered security operations firm, have launched an AI-powered cyber defense initiative in Ahmedabad, combining threat intelligence, investigation and endpoint enforcement through a joint managed security model. The AI-Powered Intelligence for Cyber Defense initiative was formally launched Tuesday at DRONA Cyber Solutions' Command and Control Centre, where the companies presented a live technical demonstration showing how an intrusion attempt can be detected, investigated and co

İlgili CVE'ler

No verified CVE link was found for this news item.

Read at the source
The Cyber Express1 mo ago

Global Crackdown on West African Crime Networks Leads to 58 Arrests

An eight-month international operation targeting West African organized crime groups has resulted in 58 arrests and the identification of 263 suspects across 22 countries, according to INTERPOL. Operation Jackal IV, conducted from November 2025 to June 2026, focused on disrupting criminal networks, tracing illicit funds, identifying high-value targets and supporting arrests and prosecutions. The operation brought together countries across six continents to tackle the growing global threat posed by West African criminal networks, including Black Axe and similar groups. These networks have been

Related Companies
İlgili CVE'ler

No verified CVE link was found for this news item.

Read at the source
The Cyber Express2 mo ago

Microsoft August 2026 Patch Tuesday Fixes 400 Flaws, Including Three Zero-days

Microsoft’s August 2026 Patch Tuesday release addresses roughly 400 security flaws across its products, including three Zero-days. One of the three is being actively exploited, while the other two were publicly disclosed before Microsoft issued fixes. The August 2026 Patch Tuesday update includes 42 vulnerabilities rated “Critical.” Of those, 37 involve remote code execution, and five involve elevation of privilege. The vulnerability breakdown is approximately 176 elevation-of-privilege flaws, 11 security-feature bypasses, 110 remote-code-execution flaws, 86 information-disclosure issues, 12 d

Read at the source
The Cyber Express2 mo ago

Gunra Ransomware Builds a New Attack Network Through RaaS

Gunra ransomware has expanded its operations through a structured ransomware-as-a-service (RaaS) affiliate program, prompting the FBI, CISA and other agencies to issue a joint advisory warning organizations about the threat. The Gunra ransomware variant uses a double-extortion model, encrypting victim data while threatening to publish stolen information on a dedicated leak site if ransom demands are not met. The FBI first observed Gunra in April 2025 as a double-extortion ransomware variant derived from leaked Conti ransomware source code. Gunra Ransomware Shifts to Affiliate Model By early 20

Related Companies
Read at the source
The Cyber Express2 mo ago

New Zealand Targets Russian Cyber Actors With Fresh Sanctions

New Zealand has announced a new round of sanctions against Russia, targeting 33 individuals and entities accused of supporting Moscow’s war against Ukraine. The latest New Zealand sanctions against Russia place particular focus on cyber actors, individuals linked to the forced relocation and re-education of Ukrainian children, and entities supporting Russia’s military-industrial complex. Foreign Minister Winston Peters said the package also targets individuals involved in creating and spreading anti-Ukraine propaganda, as well as actors from the Democratic People’s Republic of Korea (DPRK) and

Related Companies
İlgili CVE'ler

No verified CVE link was found for this news item.

Read at the source
The Cyber Express2 mo ago

Suisun City Declares Emergency After Cyberattack Disrupts Systems

The Suisun City emergency declared by local officials followed a cyberattack that forced the Northern California municipality to shut down its information technology network, disrupting some communications used by public safety agencies. The incident has placed the California city of roughly 30,000 residents among communities confronting the growing threat of cyberattacks against essential local services. The Suisun City Council declared a state of emergency Saturday after the attack compromised the city's computer systems. Officials said the network shutdown was necessary to contain the threa

İlgili CVE'ler

No verified CVE link was found for this news item.

Read at the source
The Cyber Express2 mo ago

AI Agent Exploits Gym System Vulnerability, Cancels Waitlist Booking in Australia

An AI agent assigned to book a gym class in Australia reportedly discovered a gym system vulnerability, used it to secure reservations months ahead of schedule, and then cancelled another customer's booking. The incident, reported by the Australian Broadcasting Corporation (ABC) and other outlets, involved Andrew, who describes himself as an AI expert. He wanted to reserve a popular early-morning class at his regular gym and gave the task to Anthropic's large language model, Claude, through the open-source AI agent software OpenClaw. Within minutes, the AI agent reportedly uncovered an authent

İlgili CVE'ler

No verified CVE link was found for this news item.

Read at the source
The Cyber Express2 mo ago

Ransomware Kingpin Gets 16 Years for Global Cyberattacks

A Ransom Cartel ransomware leader has been sentenced to 16 years in prison after being convicted of conspiracy to commit offenses against the United States, conspiracy to commit wire fraud, and aggravated identity theft, according to the U.S. Department of Justice. Maksim Silnikau, a 40-year-old Belarusian national, was identified in court documents as the creator and administrator of the Ransom Cartel ransomware strain, which was developed in 2021. Silnikau had been active on Russian-speaking cybercrime forums since at least 2005 and was also a member of the cybercrime website Direct Connecti

Related Companies
İlgili CVE'ler

No verified CVE link was found for this news item.

Read at the source
The Cyber Express2 mo ago

Levi Strauss Hit by Cyberattack, Corporate Files Accessed

Levi Strauss cyberattack has exposed certain corporate information after an unauthorized third party gained access to company files through compromised employee computers, according to a filing with the U.S. Securities and Exchange Commission. Levi Strauss & Co. said it recently detected a cybersecurity incident involving unauthorized access to three company-issued computers. The company said the access was enabled through social engineering techniques, allowing the attackers to reach company files. According to the filing, the company initiated its response protocols after detecting the i

Related Companies
İlgili CVE'ler

No verified CVE link was found for this news item.

Read at the source
The Cyber Express2 mo ago

The Cyber Express Weekly Roundup: Ransomware Surge, Government Data Breaches, Logistics Disruptions, and Third-Party Security Risks

This weekly roundup highlights the growing cybersecurity risks affecting businesses, government agencies, and critical service providers. From the continued dominance of ransomware operations to government database breaches and third-party supply chain incidents, recent events demonstrate how attackers are increasingly targeting trusted systems and external service providers to maximize disruption and data exposure. The latest developments reinforce that cyber threats are no longer limited to direct attacks on organizations. Threat actors are exploiting ransomware-as-a-service ecosystems, comp

İlgili CVE'ler

No verified CVE link was found for this news item.

Read at the source

41-50 / 70 news items shown