Siber Güvenlik Haberleri

Güvenilir yayınlardan canlı haberler, DayBreach CVE verileriyle eşleştirilmiş olarak.

Rapid72 ay önce

Rapid7 Analysis: Unauthenticated Remote Code Execution in JetBrains TeamCity (CVE-2026-63077)

OverviewOn July 27, 2026, JetBrains published a security advisory for CVE-2026-63077, a critical unsafe deserialization vulnerability affecting JetBrains TeamCity. An attacker who can reach a TeamCity server over HTTP or HTTPS can exploit the agent polling protocol without credentials and execute operating system commands with the privileges of the TeamCity server process.JetBrains reported no known active exploitation when it disclosed the vulnerability. However, on August 5, 2026, CISA added CVE-2026-63077 to its Known Exploited Vulnerabilities (KEV) catalog, confirming exploitation in the w

İlişkili Şirketler
İlgili CVE'ler
Kaynakta oku
Rapid72 ay önce

CVE-2026-18577: N-able N-central Authentication Bypass Exploited in the Wild

OverviewOn August 2, 2026, N-able published a security advisory for CVE-2026-18577, an authentication bypass vulnerability affecting N-central that was discovered being exploited in-the-wild after an incomplete fix for an earlier authentication bypass issue, CVE-2026-18556 was disclosed. CVE-2026-18577 allows a remote unauthenticated attacker to bypass authentication and obtain administrative control of vulnerable N-central servers in affected deployments.N-able N-central is a widely deployed Remote Monitoring and Management (RMM) platform used by managed service providers (MSPs) and enterpris

İlişkili Şirketler
Kaynakta oku
Rapid72 ay önce

Rapid7 Analysis: KindaRails2Shell (CVE-2026-66066)

OverviewOn July 29, 2026, the Ruby on Rails project published a security advisory for CVE-2026-66066, an arbitrary file read in Active Storage applications that use the Vips image processor with untrusted uploads. The affected Active Storage ranges are < 7.2.3.2, >= 8.0, < 8.0.5.1, and >= 8.1, < 8.1.3.1. Vips is the default Active Storage variant processor for applications that load Rails 7.0 or later defaults. Rails 6 applications are affected only when they explicitly configure Vips.Our Emergent Threat Response blog covers the affected versions, mitigation guidance, and curren

İlişkili Şirketler
İlgili CVE'ler
Kaynakta oku
Rapid72 ay önce

Metasploit Pro 5.1 Released

Today marks the release of Metasploit Pro 5.1 - building upon the foundation laid in 5.0, adding new evasion primitives for HTTP Meterpreter payloads, support for tracking service hierarchies, a deeper and more interactive Network Topology view, and continuing our commitment to a modern, consistent UI. This release is powered by Metasploit Framework 6.5.Malleable C2 ProfilesOne of the most requested capabilities in modern red-team engagements is the ability to blend Meterpreter's network traffic into legitimate-looking patterns. Metasploit Pro 5.1 brings full Malleable C2 profile support, powe

İlgili CVE'ler

Bu haber için doğrulanmış CVE bağlantısı bulunamadı.

Kaynakta oku
Rapid72 ay önce

Rapid7 Expands UK and Ireland Channel Presence Through Strategic Partnership with Exclusive Networks

Ross Baker is Senior Director, Northern Europe at Rapid7.As organizations across the United Kingdom and Ireland embrace AI, cloud technologies, and digital transformation in the name of enhancing customer experiences and accelerating business growth, the cybersecurity landscape must continue to evolve just as quickly.In this environment, business leaders still expect security to enable innovation, not slow it down. They're pushed to reduce risk, improve visibility across expanding attack surfaces, and respond faster than ever before, with limited resources now table stakes. This is precisely w

İlişkili Şirketler
İlgili CVE'ler

Bu haber için doğrulanmış CVE bağlantısı bulunamadı.

Kaynakta oku
Rapid72 ay önce

Rapid7 at Black Hat USA 2026: See preemptive security in action

Black Hat USA returns to Mandalay Bay in Las Vegas this August, bringing together security practitioners, researchers, and leaders from around the world. Rapid7 will be there in the Business Hall, with new capabilities, live demonstrations, expert-led sessions, and two days of activities at the Border Grill.This year, our focus is preemptive security: helping security teams anticipate credible risk, respond at machine speed, and maintain an accurate view of their security and compliance posture as their environment changes.Visit the Rapid7 booth at Black Hat USAYou can find Rapid7 at booth #24

İlgili CVE'ler

Bu haber için doğrulanmış CVE bağlantısı bulunamadı.

Kaynakta oku
Rapid72 ay önce

KindaRails2Shell: CVE-2026-66066, Critical Arbitrary File Read and Possible Remote Code Execution in Ruby on Rails

OverviewOn July 29, 2026, the Ruby on Rails project published a security advisory for CVE-2026-66066, a critical vulnerability affecting Active Storage image processing when used in conjunction with the libvips image processing library. The vulnerability has a CVSSv4 score of 9.5 and is classified as Initialization of a Resource with an Insecure Default (CWE-1188). An unauthenticated attacker may be able to leverage CVE-2026-66066 and read files accessible to the Rails application process, potentially exposing secrets that could enable remote code execution (RCE) or access to connected systems

İlgili CVE'ler
Kaynakta oku
Rapid72 ay önce

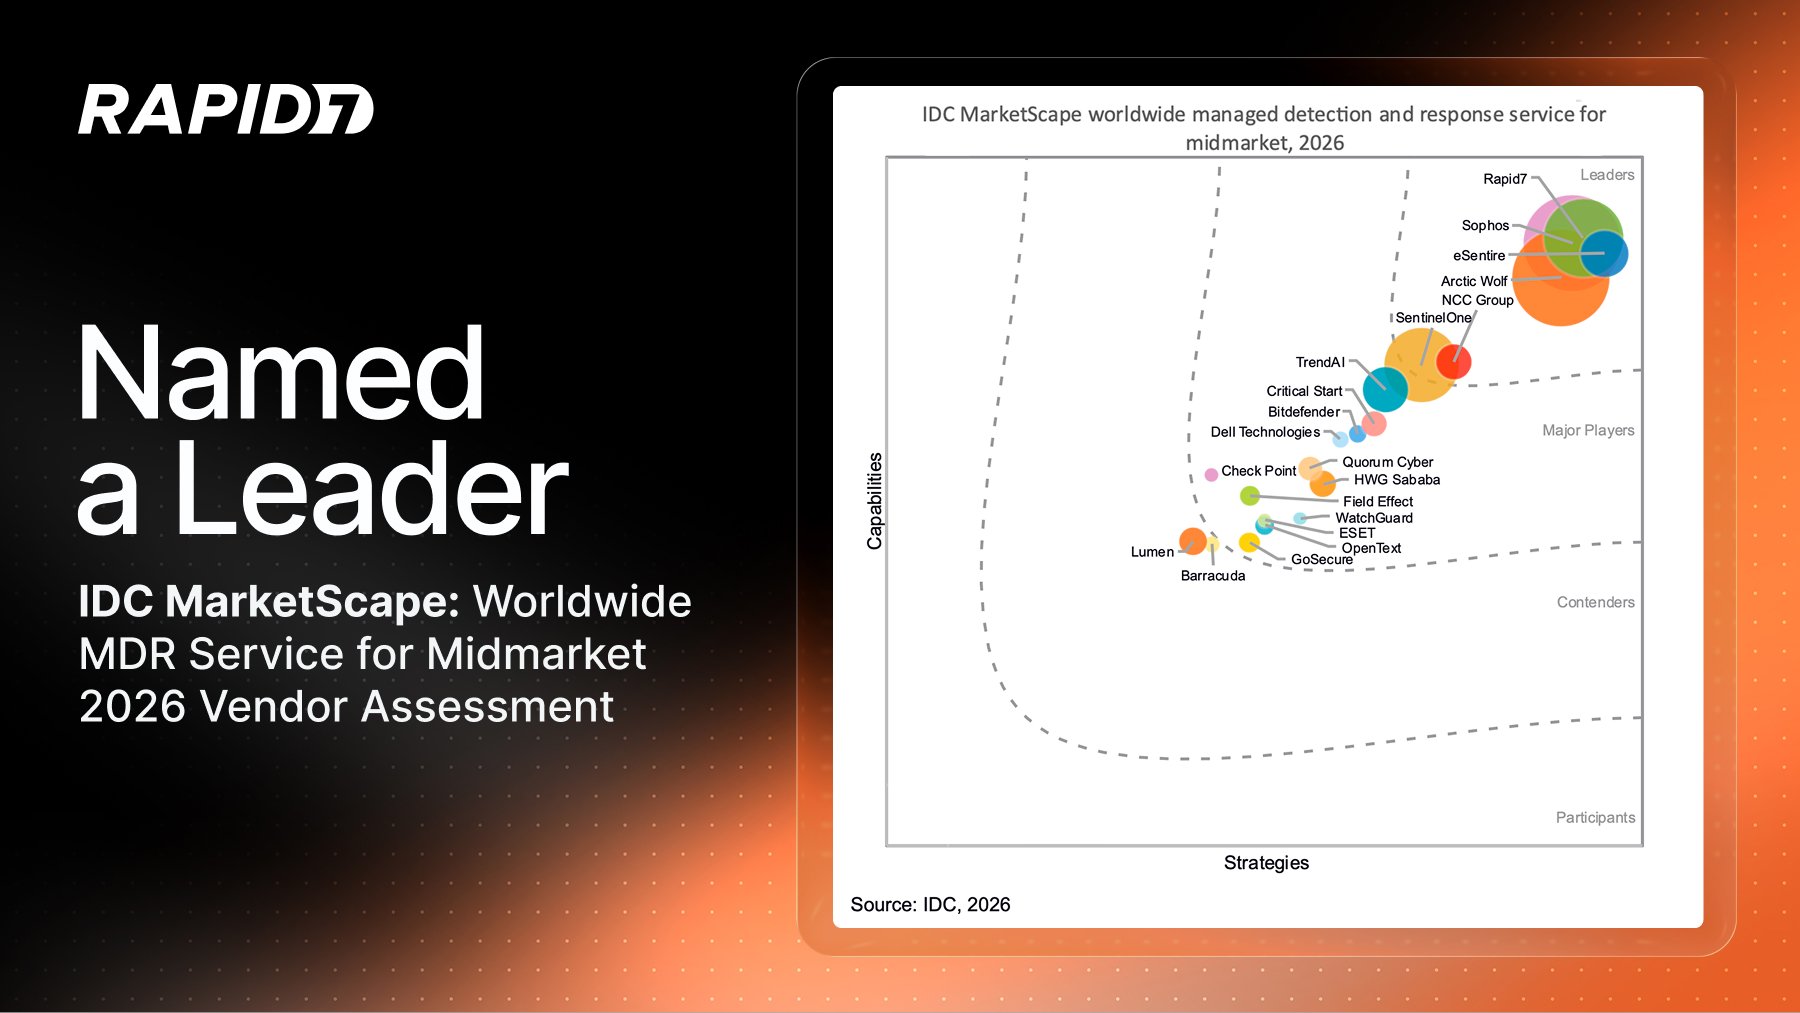
Rapid7 named a Leader in the IDC MarketScape: Worldwide MDR Service for Midmarket 2026 Vendor Assessment

IDC has named Rapid7 a Leader in the 2026 Worldwide Managed Detection and Response Service for Midmarket 2026 Vendor Assessment (Doc #US52992326, July 2026). We believe this recognition and research highlights where MDR is heading.Many security programs are still built around a reactive sequence of detect, triage, and respond, but the timelines surrounding modern attacks have changed too quickly for that model to hold up on its own. Time-to-exploit has dropped from two years to 22 hours, while eCrime breakout time now sits at 29 minutes. In an environment like that, a program moving at human s

İlişkili Şirketler
İlgili CVE'ler

Bu haber için doğrulanmış CVE bağlantısı bulunamadı.

Kaynakta oku
Rapid72 ay önce

Metasploit Framework 6.5 Released

Today we’re proud to announce that Metasploit Framework version 6.5 has been released. Over the past two years, with the help of countless contributors, we’ve added 422 new modules along with a whole slew of new features.Malleable C2 Profiles for HTTPOne of the latest and most requested features is support for Malleable C2 profiles across all current Meterpreter payloads. This feature enables users to load a standard profile into Meterpreter and change the shape of its HTTP(S) traffic. All Meterpreters, including Windows, Java, Python, PHP and Linux, have been updated with this functionality.

İlgili CVE'ler

Bu haber için doğrulanmış CVE bağlantısı bulunamadı.

Kaynakta oku
Rapid72 ay önce

Critical VMware vCenter Vulnerabilities Allow Authentication Bypass and Remote Code Execution (CVE-2026-59309, CVE-2026-59310)

OverviewOn July 29, 2026, Broadcom published security advisory VMSA-2026-0006 addressing multiple vulnerabilities in several VMWare products. Included in the advisory are two critical remotely exploitable vulnerabilities affecting VMware vCenter Server: CVE-2026-59309 and CVE-2026-59310. Both vulnerabilities carry CVSSv3.1 base scores of 9.8 and can be exploited by unauthenticated attackers with network access to a vulnerable vCenter Server.CVECVSSv3.1Description SummaryCVE-2026-593099.8 (Critical)An authentication bypass vulnerability in the VMware Directory Service of vCenter that could allo

İlişkili Şirketler
Kaynakta oku

41-50 / 62 haber gösteriliyor