Siber Güvenlik Haberleri

Güvenilir yayınlardan canlı haberler, DayBreach CVE verileriyle eşleştirilmiş olarak.

The Cyber Express1 ay önce

Boston Scientific Cyberattack Limited to Unauthorized Access on Certain On-Premises Systems

As per Boston Scientific’s Aug. 30 update, “the unauthorized activity is limited to certain on-premises systems,” providing the clearest indication yet of the scope of the cybersecurity incident that has disrupted the medical device maker’s global network and business operations. Boston Scientific said the investigation into the disruption remains ongoing, with third-party cybersecurity experts. Based on its investigation to date, the company said it has found no indication of unauthorized activity in its environment related to the incident since Aug. 25. The company also clarified that its cl

İlişkili Şirketler
İlgili CVE'ler

Bu haber için doğrulanmış CVE bağlantısı bulunamadı.

Kaynakta oku
The Cyber Express1 ay önce

PaperCut Issues Second Emergency Patch as Researchers Break Fix for Exploited Zero-Days

PaperCut released a second emergency patch last Friday, for two vulnerabilities in its NG and MF print management servers that attackers are already exploiting, after security researchers demonstrated that the vendor's first fix could be bypassed. The two flaws work as a chain. CVE-2026-81578, rated 8.8 on the CVSS scale, is an improper access control weakness in the PaperCut web management interface that lets unauthenticated remote requests reach administrative functions before the server finishes validating access. CVE-2026-82078, rated 9.4, is an unsafe dynamic class-loading flaw in the pro

İlişkili Şirketler
Kaynakta oku
The Cyber Express1 ay önce

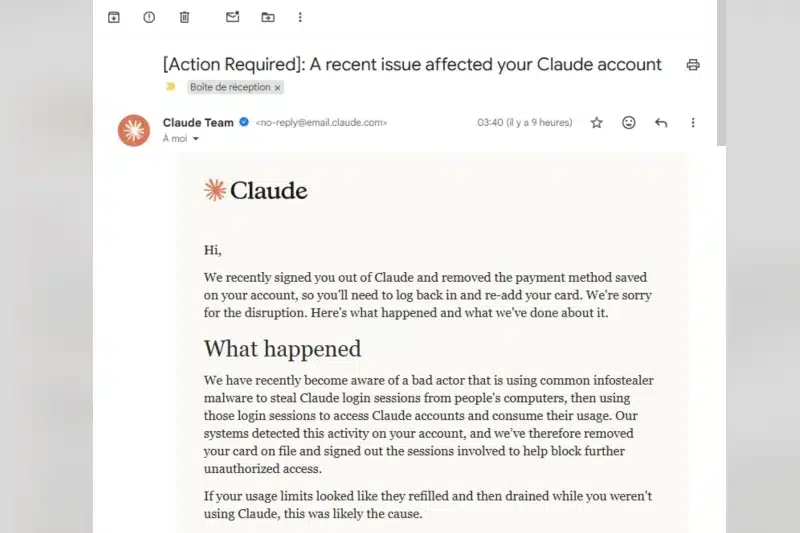
Anthropic Warns Commodity Infostealers Are Hijacking Claude Sessions to Drain Paid Usage

Anthropic warned users over the weekend that a threat actor is using widely available infostealer malware to hijack active Claude login sessions from infected computers, then using those sessions to run up victims' paid usage without ever needing a password or a two-factor code. The company said it identified six malware families in the campaign: Vidar, LummaC2, StealC, RedLine and Acreed on Windows, and Atomic Stealer, known as AMOS, on a smaller number of macOS machines. None are novel or bespoke. All are commodity stealers sold or rented on criminal dark web marketplaces, and all work the s

İlişkili Şirketler
İlgili CVE'ler

Bu haber için doğrulanmış CVE bağlantısı bulunamadı.

Kaynakta oku
The Cyber Express1 ay önce

AshSqlite Vulnerability (CVE-2026-77846) Exposes Hidden JSON Fields

CVE-2026-77846, a newly disclosed AshSqlite vulnerability, can allow attackers to access hidden or sensitive fields stored inside JSON and map columns when applications pass untrusted input to AshSqlite's get_path/2 functionality. The Erlang Ecosystem Foundation's CNA issued the vulnerability entry on August 30, 2026. The issue affects AshSqlite, the SQLite data layer used by the Ash Framework. Although it involves database queries, CVE-2026-77846 is not SQL injection. Instead, the AshSqlite vulnerability results from unsafe construction of JSON paths and the way SQLite interprets special char

İlgili CVE'ler
Kaynakta oku
The Cyber Express1 ay önce

The Cyber Express Weekly Roundup: Exploited Entra ID Flaw, AI Agent Risks, and Global Cybercrime Crackdown

This weekly roundup highlights a broad range of cybersecurity and technology developments affecting cloud identity infrastructure, social media platforms, businesses, digital assets, and international law enforcement. From a critical Microsoft Entra ID vulnerability exploited before remediation to a global crackdown on West African cybercrime networks, recent developments demonstrate how attackers continue to target both technical systems and human trust. The latest developments also show that cybersecurity risks are expanding alongside the rapid adoption of cloud services and artificial intel

İlgili CVE'ler
Kaynakta oku
The Cyber Express1 ay önce

Can We Trust AI Agents With Security Decisions? Adarsh Kant Sinha Explains

As organizations race to move from AI chatbots and copilots toward autonomous AI agents, security leaders are being forced to answer a harder question than "should we adopt AI?" — it's "can we trust AI to make security decisions?" To unpack this, The Cyber Express sat down with Adarsh Kant Sinha, Founder and CEO of ANVE.AI. With expertise spanning AI architecture, Agentic AI, AI automation, and secure AI infrastructure, Adarsh brings a practitioner's and builder's perspective to the rapidly evolving AI landscape. He has built a community of more than 25,000 ethical hackers, mentored startups,

İlişkili Şirketler
İlgili CVE'ler

Bu haber için doğrulanmış CVE bağlantısı bulunamadı.

Kaynakta oku
The Cyber Express1 ay önce

Boston Scientific Cyberattack Disrupts Order Processing, Shipping Worldwide

Boston Scientific said a cyberattack detected this Tuesday, caused a network outage and cut off its ability to process and ship customer orders globally, and the medical device maker has not been able to say when full service will return. The company disclosed the incident in an 8-K filed with the Securities and Exchange Commission on Wednesday and in a statement on its official website. It said the intrusion affected certain information technology systems and limited access to business applications underpinning day-to-day operations. Boston Scientific is among the world's largest medical devi

İlgili CVE'ler

Bu haber için doğrulanmış CVE bağlantısı bulunamadı.

Kaynakta oku
The Cyber Express1 ay önce

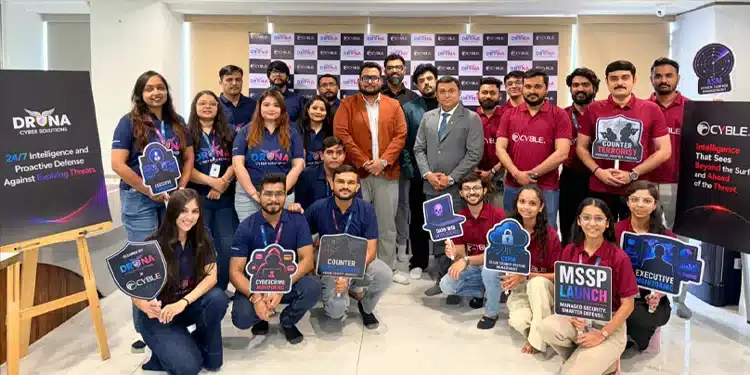
Cyble and DRONA Launch New Push to Close India’s Cybersecurity Gap

AHMEDABAD (INDIA) — Cyble, the global AI-native cybersecurity company, and DRONA Cyber Solutions, the Ahmedabad-headquartered security operations firm, have launched an AI-powered cyber defense initiative in Ahmedabad, combining threat intelligence, investigation and endpoint enforcement through a joint managed security model. The AI-Powered Intelligence for Cyber Defense initiative was formally launched Tuesday at DRONA Cyber Solutions' Command and Control Centre, where the companies presented a live technical demonstration showing how an intrusion attempt can be detected, investigated and co

İlgili CVE'ler

Bu haber için doğrulanmış CVE bağlantısı bulunamadı.

Kaynakta oku
The Cyber Express1 ay önce

Global Crackdown on West African Crime Networks Leads to 58 Arrests

An eight-month international operation targeting West African organized crime groups has resulted in 58 arrests and the identification of 263 suspects across 22 countries, according to INTERPOL. Operation Jackal IV, conducted from November 2025 to June 2026, focused on disrupting criminal networks, tracing illicit funds, identifying high-value targets and supporting arrests and prosecutions. The operation brought together countries across six continents to tackle the growing global threat posed by West African criminal networks, including Black Axe and similar groups. These networks have been

İlişkili Şirketler
İlgili CVE'ler

Bu haber için doğrulanmış CVE bağlantısı bulunamadı.

Kaynakta oku
The Cyber Express2 ay önce

Microsoft August 2026 Patch Tuesday Fixes 400 Flaws, Including Three Zero-days

Microsoft’s August 2026 Patch Tuesday release addresses roughly 400 security flaws across its products, including three Zero-days. One of the three is being actively exploited, while the other two were publicly disclosed before Microsoft issued fixes. The August 2026 Patch Tuesday update includes 42 vulnerabilities rated “Critical.” Of those, 37 involve remote code execution, and five involve elevation of privilege. The vulnerability breakdown is approximately 176 elevation-of-privilege flaws, 11 security-feature bypasses, 110 remote-code-execution flaws, 86 information-disclosure issues, 12 d

Kaynakta oku

31-40 / 67 haber gösteriliyor